An AI Agent Needs an Identity, Not Just an API Key
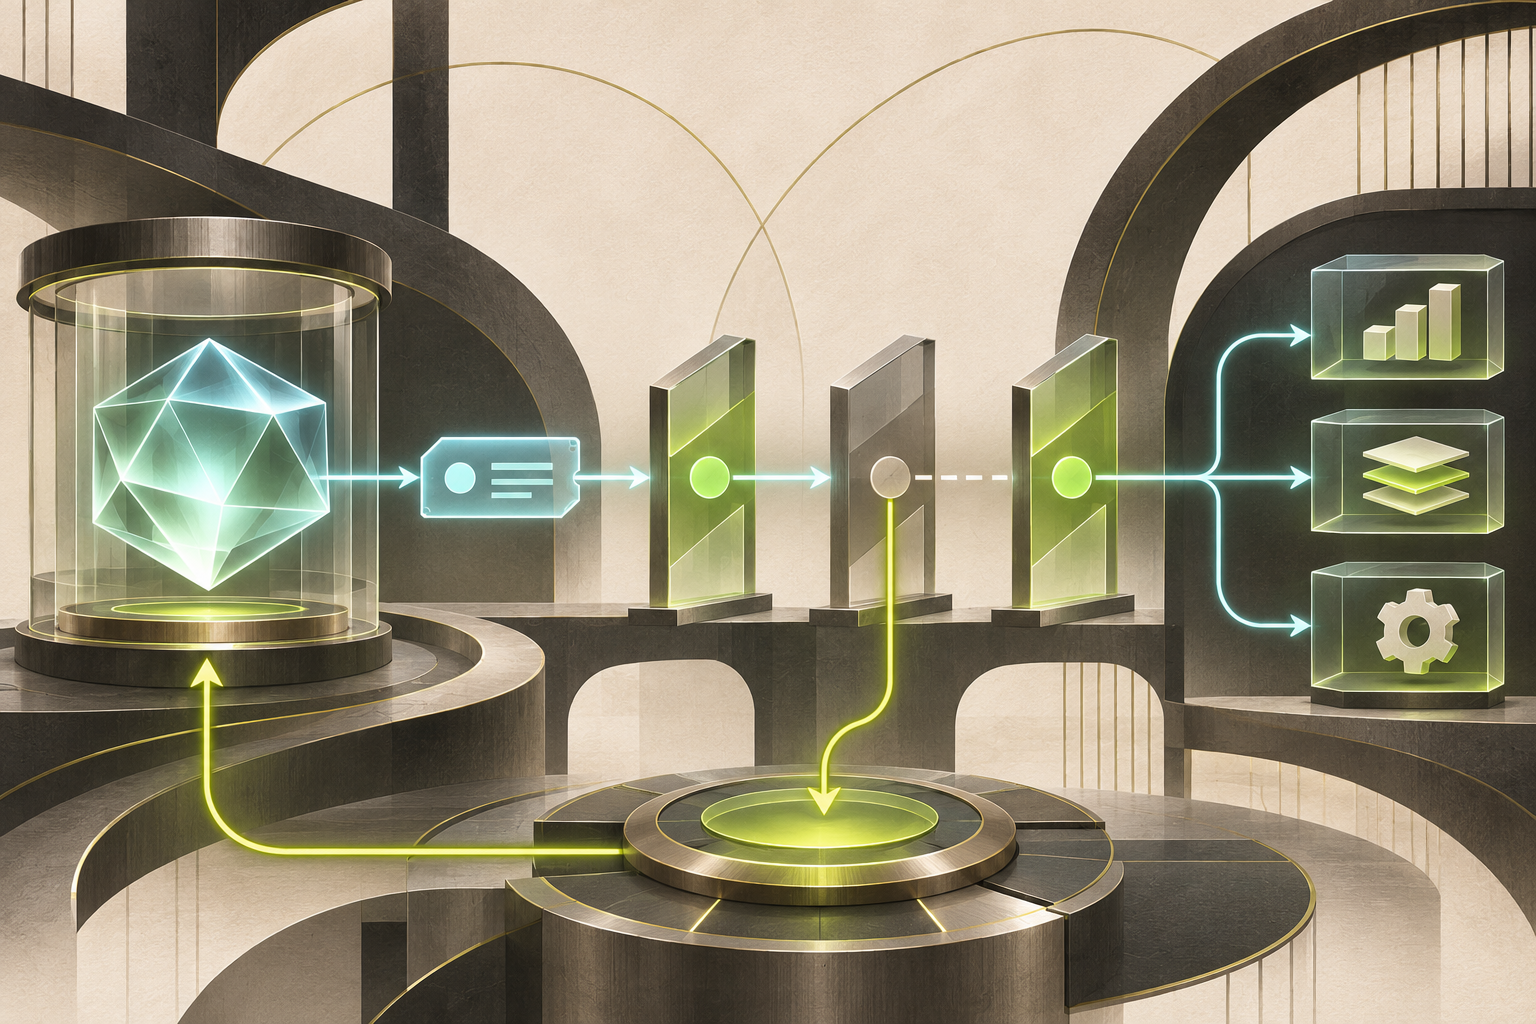
When an AI agent only summarizes a document, a mistake is a quality problem. When it reads a CRM, changes an entitlement or initiates a payment, the same mistake becomes an identity event. The answer is not a more careful prompt. It is an architecture in which the agent is a distinct principal, receives task-bound authority, is re-checked at every tool and can be interrupted mid-run. This framework translates NIST's October 27 design tenets and OWASP's November 10 builder and defender guide into product and engineering decisions.
1. A distinct agent identity is the basis of accountability
The convenient shortcut is to run an agent as the user. Integration is fast, but the system can no longer tell whether the person clicked a button, the agent acted autonomously or a sub-agent performed the operation. NIST proposes unique, cryptographically verifiable identification tied to a workload, environment and approved configuration. An agent therefore needs its own principal, credential lifecycle and identifiable versions of its policy and tools. This identity is not a display name. It must appear in API requests, audit events, approval records and operational consoles. The minimum record links the agent to the person or organization that initiated the task, the execution version, workspace and affected system. After an incident, a team should answer four questions: who requested, who decided, who executed and under what authority. Without that separation, autonomy scales throughput while erasing responsibility.
2. Authority should exist for a task, not wait in a drawer
A long-lived API key gives the agent power even when it has no task. If a key leaks, a malicious prompt changes intent or a tool is compromised, the attacker receives a large operating window. NIST emphasizes zero standing privilege and authorization that is short-lived, dynamic, revocable and audience-specific. The agent starts with no access and receives a grant only after a defined task is created. The grant names the action, resource, data boundary, destination, amount limit, expiry and context. Reading a balance is not permission to transfer funds; opening one customer record is not database access. Infrastructure issues an ephemeral token for each step or narrow set of operations and binds it to one destination service. Leakage becomes a bounded event rather than persistent access, and the organization can measure how much authority was issued and used.
3. Delegation is an authority contract, not a shared secret
Many agents split work across sub-agents, tools and external services. The chain becomes dangerous when every participant inherits the parent's full permissions. NIST calls for attenuation: authority may only become narrower as it moves downstream. A sub-agent assembling a document can read selected files but does not need permission to send it. An address-validation service does not need a complete account record. Represent the task as a signed mandate containing the intended outcome, constraints, forbidden actions, expiry and originator. Each component receives a narrow derivative, and each transition records what was delegated and why. A destination can then verify intent without trusting text generated by the model. For a product team, the mandate becomes an operational contract that can be shown, tested and reconstructed instead of a hidden sentence inside a prompt.
4. Human approval must be bound to the exact action
A generic Approve button is not control. The reviewer needs to see which agent is acting, the exact resource and operation, what changed after the request, the cost and whether the result can be reversed. Approval should be signed against a canonical payload. If the destination, amount or parameters change, approval expires. The agent cannot obtain consent for one description and execute another action. Not every call needs a person. Excessive approvals cause consent fatigue and turn review into ritual. Define triggers by impact, reversibility, sensitivity and deviation from normal behavior. A bounded read can proceed automatically; an entitlement change, external message or payment needs review. Measure approvals, rejections, modifications and decision time. If people approve nearly everything automatically, the control path is not protecting the system and should be redesigned.
5. Every tool is a policy-enforcement point
The model may propose an action; it is not the source of truth for whether the action is allowed. NIST stresses architectural separation between reasoning and policy because a model receives data and instructions in the same token stream and may interpret hostile content as a command. Credentials stay out of prompts, and every tool call passes through a deterministic layer that checks identity, scope, destination, time, system state and required approval. Authorization is repeated for every invocation, not only at session start. An agent that was valid one minute ago may have left its mandate, crossed a risk threshold or continued after revocation. Tools need explicit deny behavior, idempotency, rate limits and structured results. A write should first produce a readable preview, while an irreversible operation needs a compensating action or manual recovery path. Prompt injection can influence reasoning, but it does not automatically expand real permissions.
6. Prompt injection is also an authorization problem
A document, webpage or customer message can tell an agent to ignore its task, expose data or call a tool. Text filters and guardrails help, but NIST says guardrails alone are insufficient. If the same agent can read a secret and send it to an arbitrary destination, an attacker only has to persuade the model. A secure architecture assumes persuasion may succeed and limits impact by separating data, policy and authority. Classify sources as trusted or untrusted, expose only task-relevant tools, separate reads from writes and prevent untrusted content from changing policy. Moving sensitive data to an external destination requires a deliberate decision at the enforcement layer. Include indirect injection in evaluations: an instruction in a PDF, CRM field, search result or another tool's response. Success is not merely that the model notices the trap; it is that the system prevents a forbidden action even when the model is wrong.
7. Service identity and business identity must stay connected
An agent can have a valid technical identity and still act for the wrong customer. In a multi-tenant system, every grant must be bound to a tenant, responsible user, business purpose and processing basis. A workload identity cannot bypass data isolation. The policy engine checks both agent and context: customer, data region, active contract and sensitivity class. The linkage also shapes user experience. Activity screens should say that a particular agent acted on behalf of a person or team rather than attributing everything to the last human who signed in. Customers need to see which agents are active, what systems they reach and how to disable them. An administrator should end one mandate without deleting a person's account and revoke one agent without breaking unrelated services. Good identity is a control interface as well as an IAM object.
8. Real audit reconstructs a decision, not just a log line
A list of tool calls does not explain why an operation was allowed. Useful audit captures the agent identity, task originator, mandate, policy version, material inputs, authorization decision, human approval, token identifier, tool result and trace link. That does not require retaining every raw prompt forever. It requires a defined evidence minimum, encryption, redaction and risk-based retention. The record should resist modification and support queries by customer, agent, task and resource. Operations teams must assemble a timeline without manually joining five systems. Periodic tests should select an action and reconstruct whether it matched policy at that moment. Useful metrics include denied calls, unused expired grants, scope violations, time to revoke and time to reconstruct an incident. The same audit foundation supports security, customer support, compliance and product learning.
9. Revocation, suspension and recovery are lifecycle features
An agent identity system is incomplete if it can issue authority but cannot stop it. It must revoke a token, mandate, agent, tool or tenant and propagate the change quickly. NIST IR 8587 emphasizes protection of tokens and assertions throughout their lifecycle, including verification, key management and continuous monitoring. For autonomous agents, revocation time is a business SLO. Exercise lost credentials, abnormal behavior, supplier compromise and a policy change during execution. The system should block future actions, determine what already happened, avoid duplicate execution and offer manual continuation or rollback. Key rotation should not change the agent's identity or erase audit. After an incident, access returns gradually with a narrower scope. Recovery is restoring capability while preserving evidence and applying boundaries learned from failure.
10. Move to production in levels of authority
There is no single jump from pilot to autonomy. Start in observe mode, where the agent recommends but cannot act; progress to scoped read-only access; then reversible writes with approval; and only later to pre-bounded operations without per-action approval. Each stage needs success and stop thresholds: task accuracy, policy violations, review time, rollback rate, cost and near misses. The production map includes an agent inventory, business and technical owners, systems, tools, data classes, scopes, approval paths, revocation and failure drills. OWASP's V2 guide covers secure architecture, identity and access controls, runtime protection, supply-chain security and assurance testing across the lifecycle. The important question is not how many steps an agent can execute. It is whether every step remains connected to an identity, an intent and authority that can be checked. That is the difference between an impressive demo and a system an organization can responsibly operate.